WordPress core RCE (CVE-2026-87902) exploited within hours of patching
Tags Policy & Law
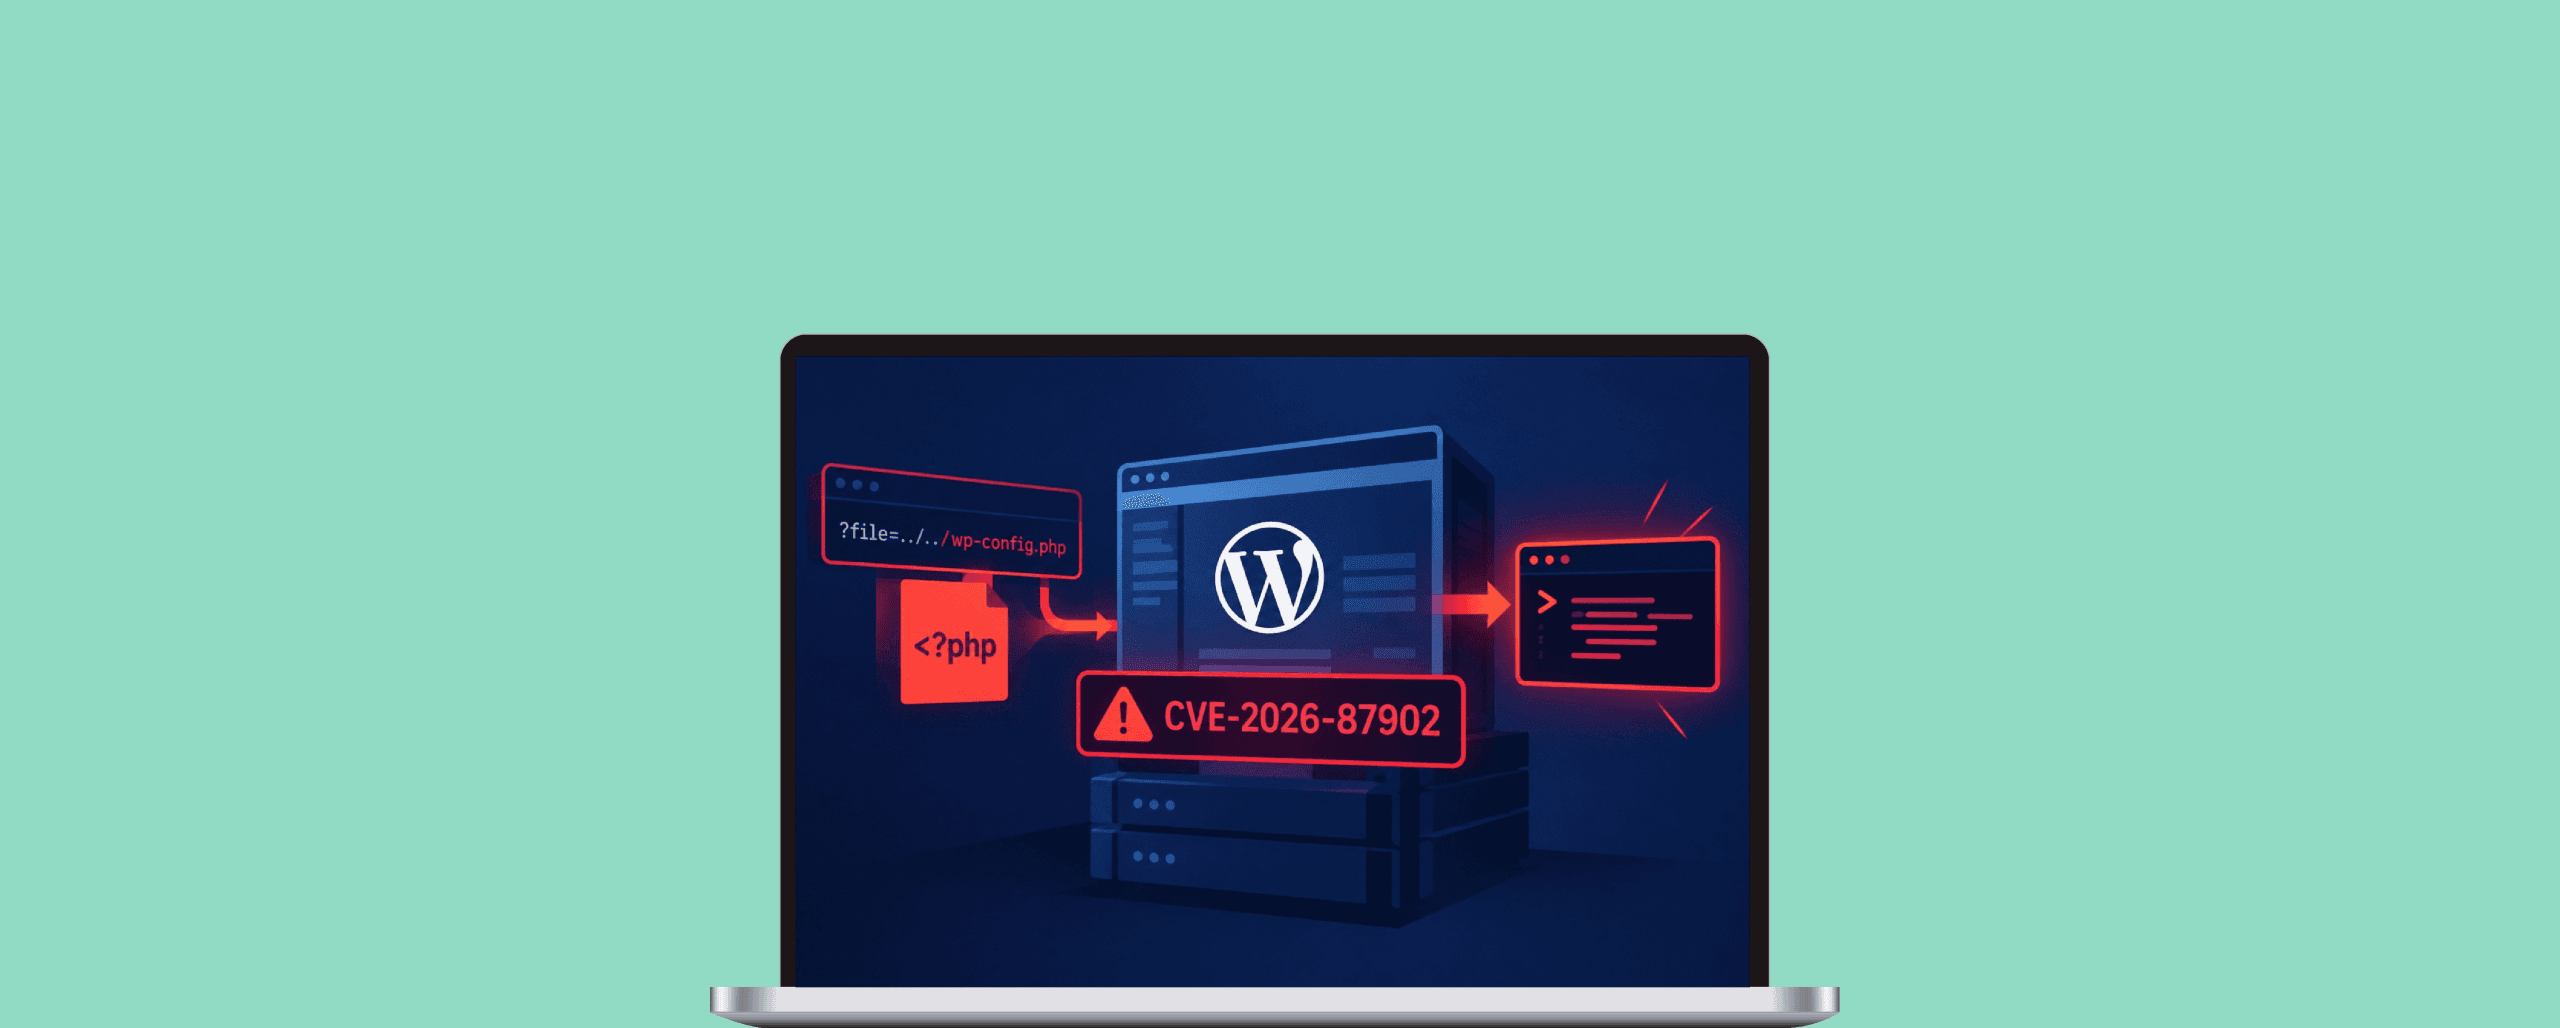
WordPress patched a critical remote code execution flaw, CVE-2026-87902, on September 22, 2026, and attackers began exploiting it the same day, progressing from reconnaissance to attempts to write malicious PHP files. The vulnerability carries a CVSS v4.0 score of 9.2 and allows unauthenticated remote attackers to force get_page_template() to include a readable local PHP file outside the active theme directories, which can become code execution under specific server and theme conditions. Affected versions span WordPress 4.7.0 through 7.1.1, with fixes backported across all release branches. CISA has added the CVE to its KEV catalog.
Technical significance
Because WordPress powers a large share of the web, an unauthenticated RCE with a public scanning template and same-day exploitation puts unpatched, internet-facing sites at immediate risk. The dependence on theme and server preconditions means exposure varies, but the KEV listing signals real-world impact.